Understand threats and change
BeyondTrust Remote Support flaw: what to ask your IT provider
What should a small business ask its IT provider about the BeyondTrust flaw?
Ask your IT provider when it patched the vulnerable appliance and what it found in records from before the fix.
The patch closes this vulnerability on a fixed appliance, but it cannot show whether someone accessed the system beforehand. Ask which records and dates the provider reviewed, and who owns any unanswered question.
BeyondTrust Remote Support is a tool IT providers use to control customers’ computers. A flaw in the software let attackers take over support appliances and use them to reach internal computers. In one investigation, Mandiant found files copied and appliance logs deleted; that does not show whether the investigated organisation’s own customers were affected 1Reference 1: ARMORY CASTLE Exploits BeyondTrust.
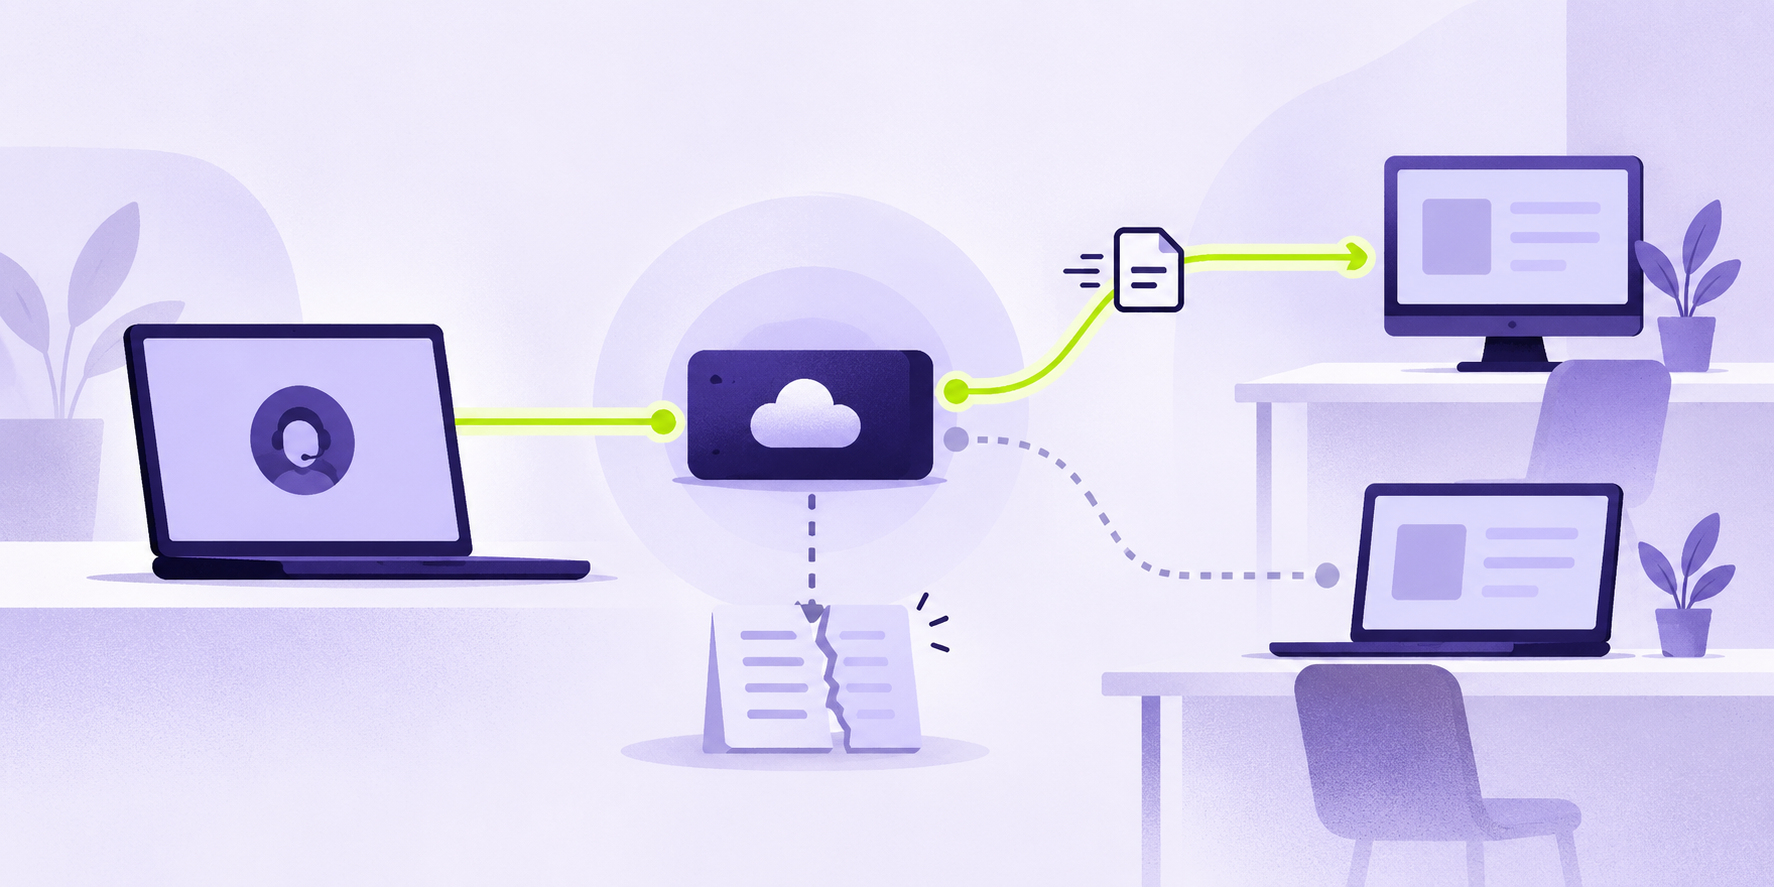
Think of a support appliance as a reception desk that can issue passes to rooms behind it. The flaw let attackers take control of that desk and start support sessions to internal computers [1]. The reports do not establish how many downstream customers were affected.
BeyondTrust says the attackers used one hosted Remote Support instance and one self-hosted appliance on 29 August 2026. It released the fix on 8 October and disclosed the vulnerability publicly on 15 October. On 16 October, the company said it knew of two affected customers 2Reference 2: ARMORY CASTLE and BT26-05: What Security Teams Need to Know. These dates and counts describe the vendor’s investigation at that time; they do not establish whether other organisations or customers were affected.
What the flaw allowed
Successful exploitation let an attacker upload files to an affected appliance 1Reference 1: ARMORY CASTLE Exploits BeyondTrust, 3Reference 3: BT26-05: Critical vulnerability in Remote Support. Mandiant found that attackers gained administrator access, changed permissions and started support sessions to internal computers [1]. BeyondTrust’s advisory says its hosted service had been patched by 9 October; customers running their own appliance needed to install the update [3].
A patch prevents this route from being used again on a fixed appliance. It does not say whether the appliance was accessed before the patch or whether someone used it to reach customer systems. Mandiant recommends reviewing internet-facing appliances that ran a vulnerable version [1].
What to ask your IT provider
Ask whether the provider uses BeyondTrust Remote Support, when the appliance supporting your systems was patched, and what its review found about earlier access.
- Do you use BeyondTrust Remote Support to connect to our computers? Is it hosted by BeyondTrust or run on your own appliance?
- When was the appliance supporting our systems patched? Was it reachable from the internet while vulnerable?
- Which dates and records did you review for earlier access? Include logs stored outside the appliance.
- Did the review find support sessions, file transfers or account changes involving our systems?
The UK NCSC’s supplier-assurance questions include how a provider would maintain service after an incident [4]. Ask for the review results in writing, with an owner and update date for anything still unresolved.
Read our Secure remote access lets authorised people use business systems from elsewhere while controlling their identity, devices and permissions.Read definition for how named people, limited permissions and logging help control support access. For broader steps to protect essential work, see our small-business cyber security guide.